
 curl -fsSL https://floci.io/install.sh | sh
Installing Floci CLI...
Downloading floci 0.4.0 for darwin-amd64...
Checksum verified.

Floci CLI 0.4.0 installed to /usr/local/bin/floci

Quick start:
  floci start            # launch Floci
  floci doctor           # check your environment
  export AWS_ENDPOINT_URL=http://localhost:4566
  aws s3 mb s3://my-bucket  # use the AWS CLI against Floci
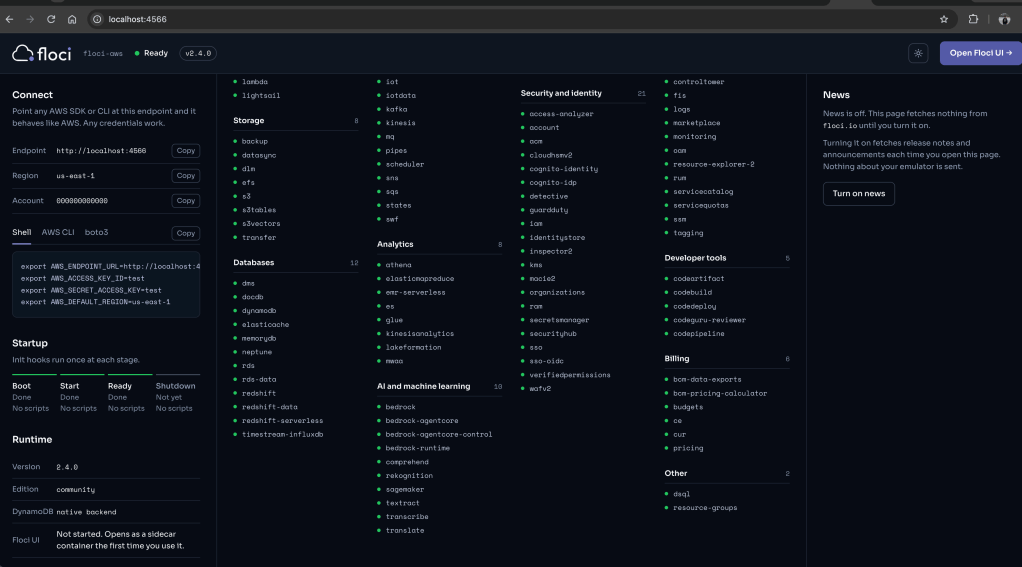
floci start Checking image floci/floci:latest (policy: missing)...latest: Pulling from floci/floci25582d7c77aa: Pulling fs layerdf21d34bd12f: Pulling fs layer324dcf10649f: Pulling fs layer39da49f3279b: Pulling fs layer9ed273b013df: Pulling fs layer616bd0c8998c: Pulling fs layer39da49f3279b: Waiting9ed273b013df: Waiting616bd0c8998c: Waiting324dcf10649f: Verifying Checksumdf21d34bd12f: Verifying Checksum324dcf10649f: Download completedf21d34bd12f: Download complete25582d7c77aa: Verifying Checksum25582d7c77aa: Download complete9ed273b013df: Download complete39da49f3279b: Verifying Checksum39da49f3279b: Download complete25582d7c77aa: Pull completedf21d34bd12f: Pull complete324dcf10649f: Pull complete39da49f3279b: Pull complete9ed273b013df: Pull complete616bd0c8998c: Verifying Checksum616bd0c8998c: Download complete616bd0c8998c: Pull completeDigest: sha256:5ee85db604c4aa74ac76e07ea5cc83086f37bb472bf3dbb97e34019e48efae9cStatus: Downloaded newer image for floci/floci:latestdocker.io/floci/floci:latestStarting Floci AWS container...Container started (a70355eaa5d3)Waiting for Floci AWS to be ready...Floci AWS is ready (http://localhost:4566)
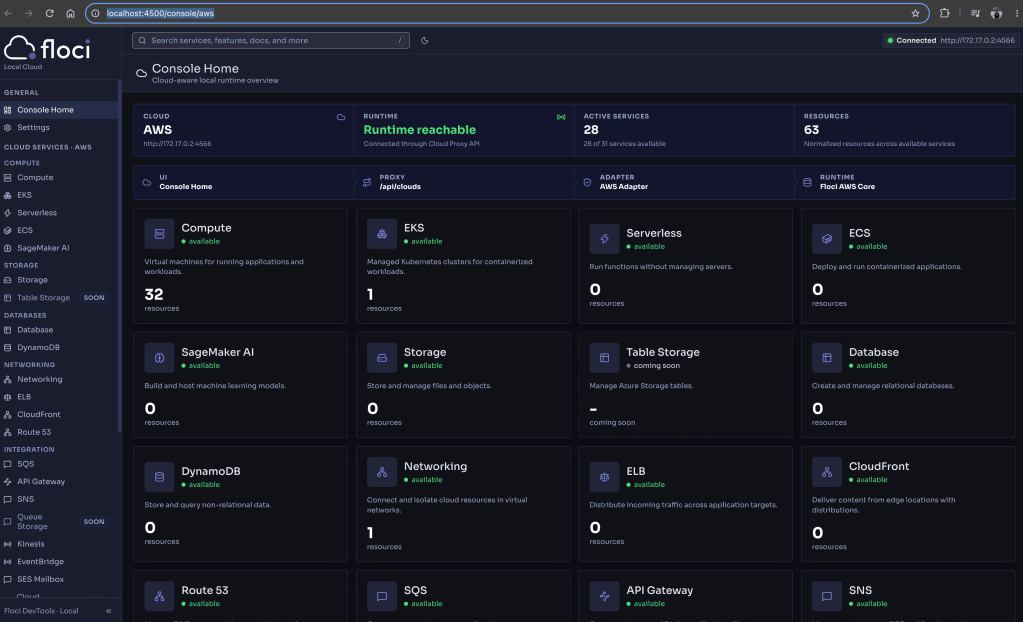
http://localhost:4500/console/aws
mkdir test-local-cluster cd test-local-cluster
export AWS_ENDPOINT_URL=http://localhost:4566export AWS_DEFAULT_REGION=us-east-1export AWS_ACCESS_KEY_ID=testexport AWS_SECRET_ACCESS_KEY=testaws eks create-cluster \ --name dev-cluster \ --role-arn arn:aws:iam::000000000000:role/eks-role \ --resources-vpc-config subnetIds=subnet-default-us-east-1-aaws eks wait cluster-active --name dev-clusteraws iam create-user --user-name eks-adminread AWS_ACCESS_KEY_ID AWS_SECRET_ACCESS_KEY <<< "$(aws iam create-access-key \ --user-name eks-admin --query 'AccessKey.[AccessKeyId,SecretAccessKey]' --output text)"export AWS_ACCESS_KEY_ID AWS_SECRET_ACCESS_KEYaws eks update-kubeconfig --name dev-clusterkubectl run nginx --image=nginx:alpine --port=80kubectl get pods,svc
kubectl get ns NAME STATUS AGEdefault Active 2m9skube-node-lease Active 2m9skube-public Active 2m9skube-system Active 2m9s kubectl get svc NAME TYPE CLUSTER-IP EXTERNAL-IP PORT(S) AGEkubernetes ClusterIP 10.100.0.1 <none> 443/TCP 113skubectl get pods NAME READY STATUS RESTARTS AGEnginx 1/1 Running 0 65shttp://localhost:4500/console/aws